CRITICAL payments-api
CrashLoopBackOff · 7 restarts
Kobi Autopilot · autonomous remediation for Kubernetes
Kobi Autopilot finds the cause, applies a fix from a closed catalog of verified actions and reverts it if the check fails. You decide how far it goes: start in suggest-only mode and raise the level as you gain trust.
In our own production: real incidents resolved with no human intervention.
A pod enters CrashLoopBackOff at 03:14; Kobi diagnoses the liveness probe, applies a catalog fix and verifies it in 87 seconds. The pager goes from critical to resolved. One time in three it is another incident, an OOMKilled on checkout-worker: Kobi raises the memory limit, verification does not pass because it is a leak, so it reverts the change and escalates to you.
AI agent · 24/7
01 · The problem
From the alert to the commit that caused it, hopping across five tools. The same incident, side by side, with Kobi.
The same incident, side by side. You: from 03:14 to 03:34, across five tools, until you find the commit that caused it. Kobi: 87 seconds to diagnose it, fix it with a catalog action, verify it and write the postmortem.
At 03:34 you know what broke it. Kobi had fixed it at 03:15.
Reconstruction of a typical incident · illustrative data · real scale: 20 min vs 87 s
Time
Twenty minutes to learn what changed. The alert doesn't say; five tools each know half of it.
Access
Access, scattered. An up-to-date kubeconfig, a VPN or a bastion per cluster, and again for every new person.
Context
Ten tabs, zero context. None of them links the event to the deploy and to the permission that explains it.
02 · How it resolves
Deterministic rules identify the covered cases and when an investigation is needed. When Kobi proposes an action, the executor only accepts operations from a closed catalog and honors the cluster's RBAC. The only thing that changes is who approves.
▶ Try it: pick a level, break something and see how far Kobi goes.
three get resolved · one reverts · one stays out
Kobi diagnoses, shows you the exact command and runs it on your click. Destructive actions always carry your signature.
Same engine: detect, diagnose, remediate. Only the control model changes.
Illustrative script using actions from the real catalog · timings follow the 03:14 incident.
Closed catalog · cluster RBAC · confidence threshold per rule · automatic rollback · everything is logged
03 · What connects
The five answers a platform team asks for before installing anything in production.
Outbound gRPC channel from inside the cluster. Your API server is never exposed: no VPN, no bastion, no open ports.
No kubeconfig on the operator's laptop. Start with metrics or read-only and move up to operator whenever you want.
No action runs without your policy. Closed catalog; destructive actions require human approval by platform policy.
If you have it, it's joined to resources, events and changes. If not, the agent uses kubelet metrics.
Only what's needed to investigate leaves the cluster. What is sent, how long it's kept and where, in the trust model.
YOUR CLUSTER · GKE, EKS, AKS, ON-PREM
KubeBolt agent
ServiceAccount · no kubeconfig
RBAC: metrics ▸ read ▸ operator
starts read-only
API server
not exposed · no VPN
Prometheus
yours, if you have one
workloads · events · logs · changes
YOUR NETWORK · FIREWALL
KubeBolt Cloud
or self-hosted on your infra
04 · Kobi, one agent, two modes
The same agent, the same closed catalog, the same log of every action. The only thing that changes is who approves.
CrashLoopBackOff since the 03:02 rollout. The ConfigMap payments-config changed DB_URL and the pod can't connect. 7 restarts, no impact on other services.
root cause the payments-config ConfigMap, in the 03:02 rollout · confidence 0.94
Copilot: you ask, Kobi answers. Managed in Cloud, your own key if you self-host, and an MCP server.
deterministic AI + deterministic model
Autopilot only handles catalogued incidents.
In our own production: real incidents resolved with no human intervention.
05 · The platform
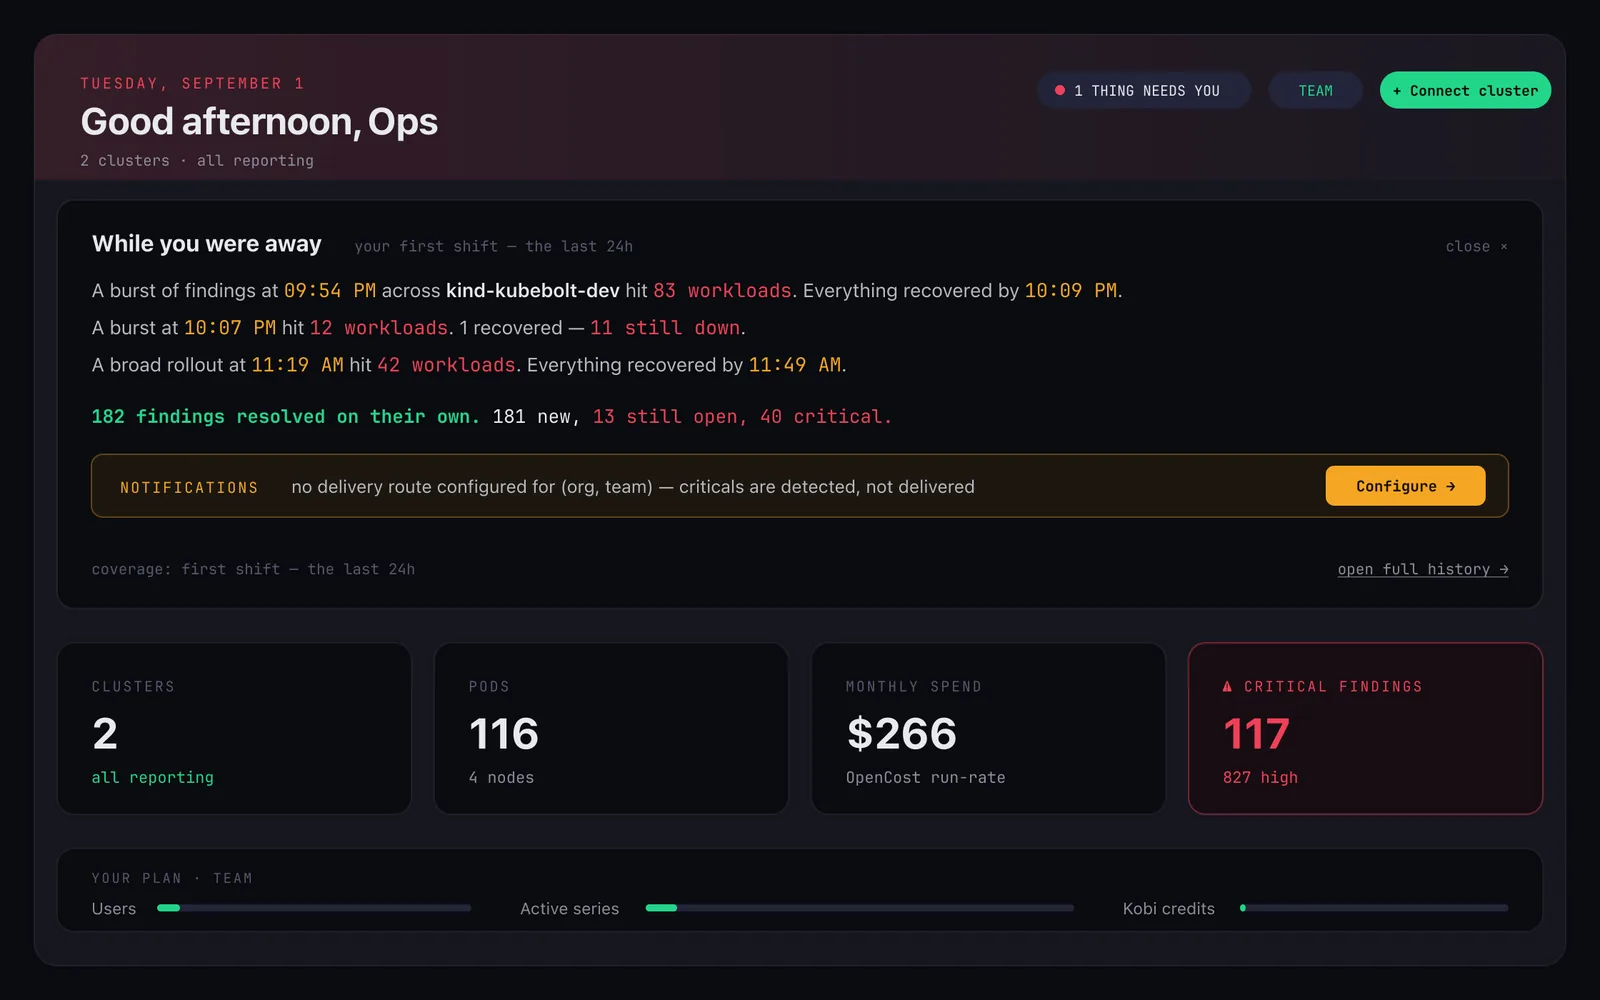
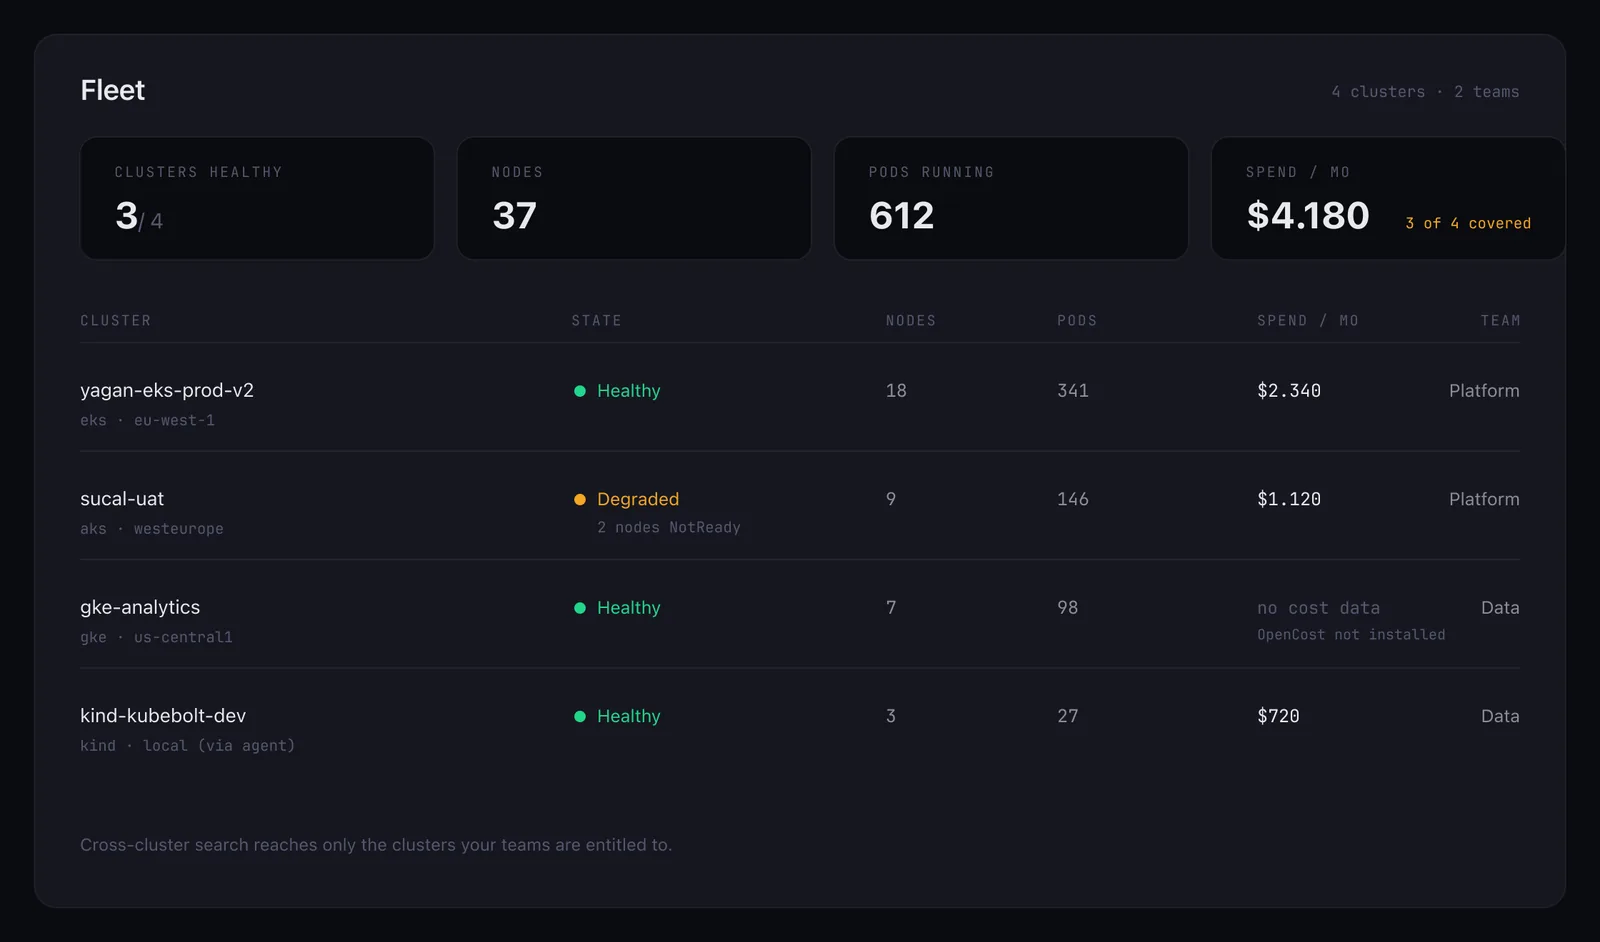
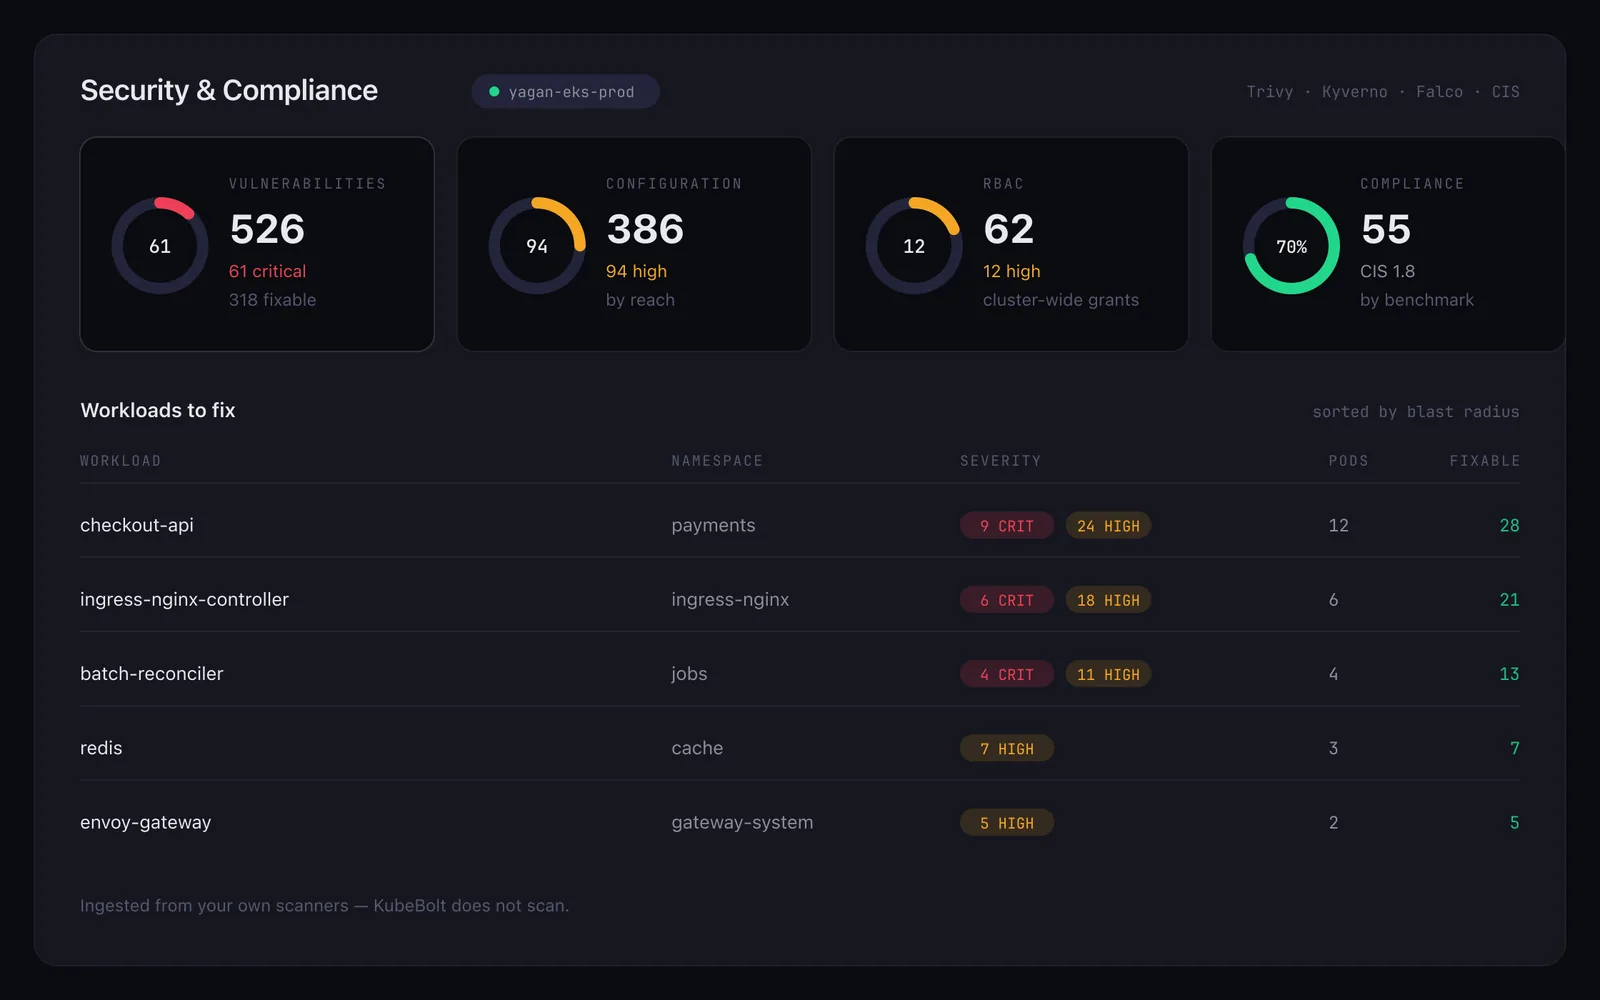
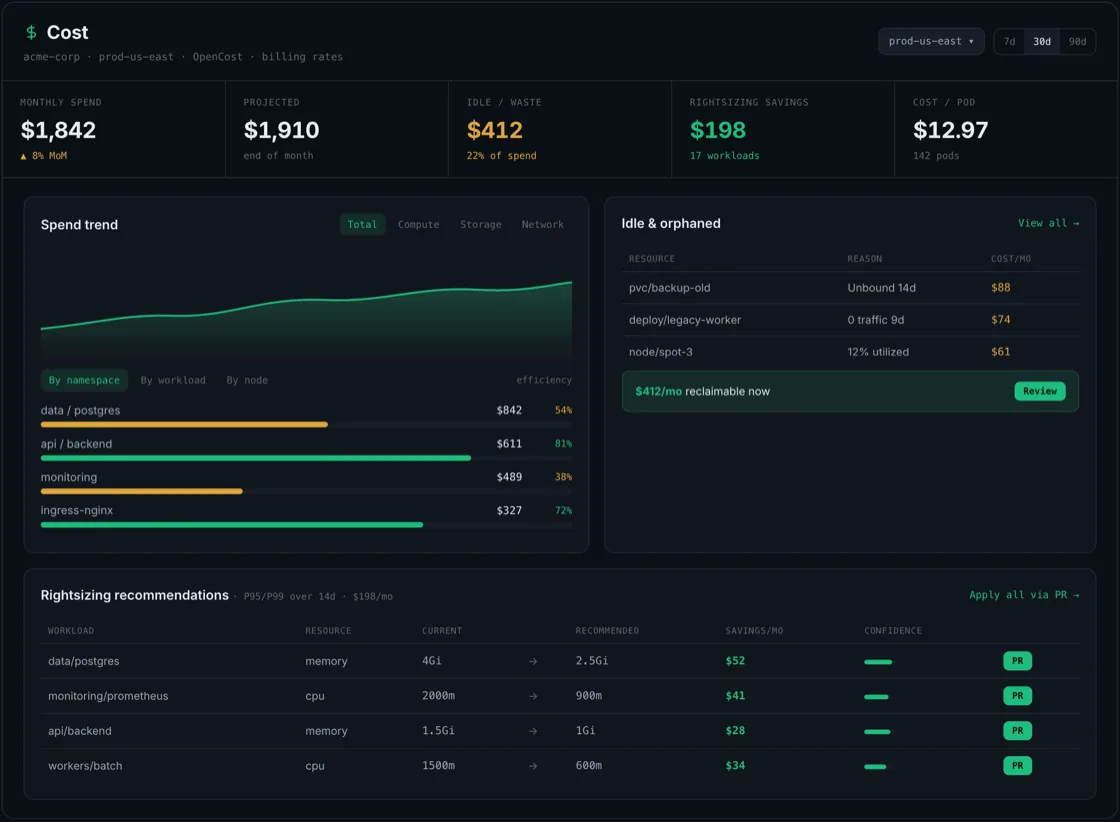
The same agent that already connects the cluster opens four views. Today, on Free.
Cluster: Overview · Capacity · Cost · Reliability
Home. What happened while you were away, what needs your attention today and the spend, across every cluster.
Fleet. Each cluster's health, nodes, pods and spend, at a glance.
Security. Vulnerabilities, RBAC and CIS from your own scanners.
Cluster · Cost. OpenCost, idle and recommended rightsizing, in beta.
06 · Open Source and Cloud
KubeBolt ships in two editions. Open Source is Apache 2.0, unlimited, on your own infra; KubeBolt Cloud adds managed Kobi Autopilot and team access with OAuth, with a free tier available now.
Open Source · Apache 2.0
No cost · you run the infra
The same agent, under Apache 2.0 and unlimited, running on your own infrastructure. Includes Kobi Copilot with your own key (BYOK).
View on GitHubSaaS · Cloud
$0 $49€45 /mo + usage
The same agent, with managed Kobi Autopilot and team access via OAuth. Enterprise Self-Hosted is this same SaaS in your infrastructure.
Start free →Included in the plan
What is charged today
Business, Enterprise and the calculator During launch, overage on nodes, pods and series is metered but not billed; AI credits pause when they run out.
Create the account, install the agent, and on the first alert you'll see Kobi working with you. Start in suggest-only.
Free · 2 clusters · no time limit
Or install the open-source agent
$ helm install kubebolt-agent \
  oci://ghcr.io/clm-cloud-solutions/kubebolt/helm/kubebolt-agent \
  --namespace kubebolt-system --create-namespace \
  --set backendUrl=agent.kubebolt.io:443 --set tls.enabled=true \
  --set auth.mode=ingest-token \
  --set auth.ingestToken.existingSecret=<secret-with-your-token> \
  --set cluster.name=<cluster-name>
The in-app wizard generates this command with your token and cluster name. docs/connect-clusters
Apache 2.0 · ★ on GitHub · the agent dials out, never in.
What's next
One note per release, no noise.
The KubeBolt AI SRE · visiting
Kobi can be wrong. Official pricing lives in the plans section.